IT: every request tracked, every grant audited.
Access requests, vendor docs and approvals live in three places and one person's head. We put them in one system an auditor will love.
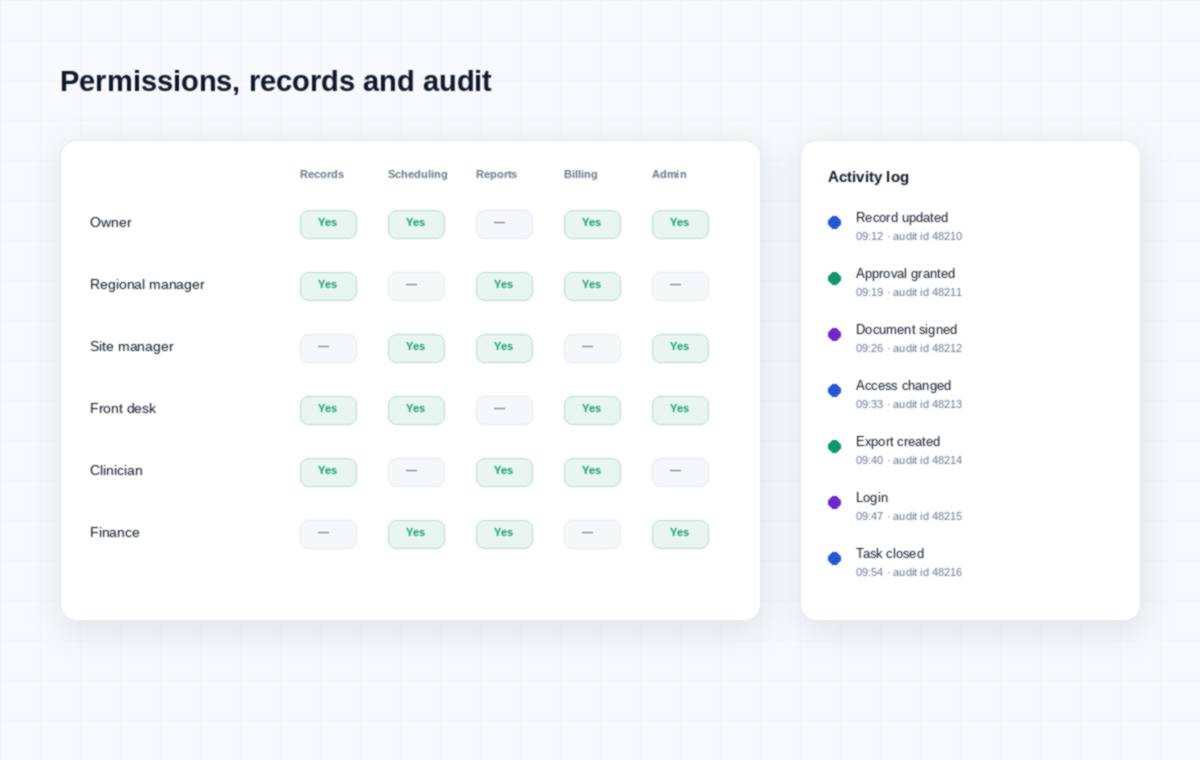
Who can see what, and who approved it
Role-based permissions across systems, granted through a request that leaves a record, and revoked automatically when someone changes role or leaves.
Role-based permissions
Per system, per site, per record type — modelled once, applied everywhere.
Joiner, mover, leaver
Access follows the HR record, so offboarding is not a memory test.
Audit-ready records
Every access change written with requester, approver, time and reason.
Vendor documentation
Contracts, renewals and contacts kept where the requests are handled.
Integration management
One inventory of what talks to what, and who owns each connection.
Operational reporting
Request volumes, resolution times and recurring causes.
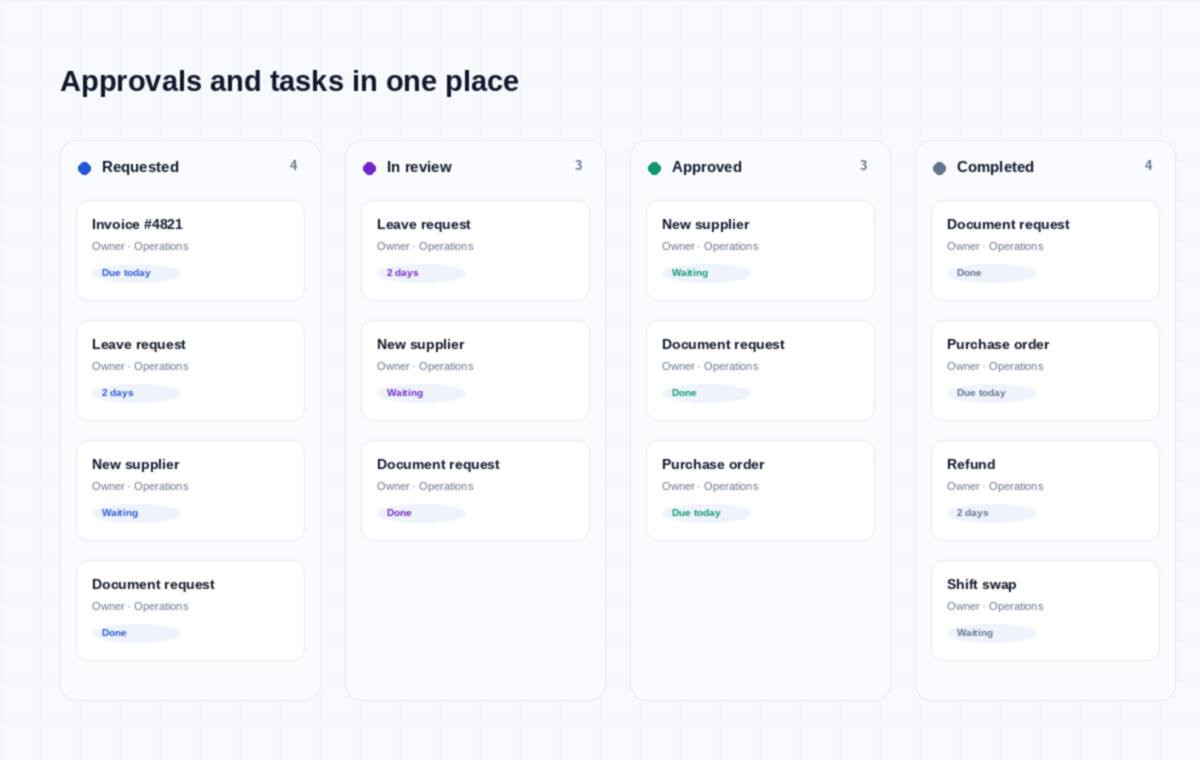
A queue beats an inbox
Requests by chat, email and corridor can't be prioritised, measured or handed over. Intake forms turn them into tracked work with a status the requester can see.
- Categorised intake with the detail needed to act, captured up front.
- Priority and ownership assigned by rule, escalated by age.
- Approval workflows for spend, access and change.
- Status visible to the requester, so nobody asks for an update.
Make IT work visible
We will map your current request paths and show you the same month running through a queue.